
Fullerton Fund Management
A Singapore asset manager needed a web partner who could pass penetration tests, not just build pages. Since 2021 we have rebuilt, migrated and hardened Fullerton's WordPress platform, and we still run it today.
Chillybin rebuilt Fullerton's WordPress platform in 2021, migrated it to the group's cloud platform in 2025 with penetration test findings remediated, and still runs it under a formal SLA.
What we were solving
Fullerton Fund Management (FFMC) is a Singapore-based asset manager serving institutions and high-net-worth investors across Asia-Pacific. Its website is not a brochure. It is where fund performance, market insights and regulatory information reach clients, so it has to look credible, load fast and stand up to formal security scrutiny.
That last part is the hard part. As a regulated financial institution, Fullerton's digital estate is subject to vulnerability assessment and penetration testing (VAPT), infrastructure standards set at group level, and change control that separates staging, UAT and production. A typical agency workflow (build it, launch it, patch it occasionally) does not survive that environment.
Fullerton needed a partner who could carry the platform through infrastructure changes and repeated security audits without breaking the publishing workflow its marketing team relies on.

How we tackled it
A publishing platform built for a fund manager
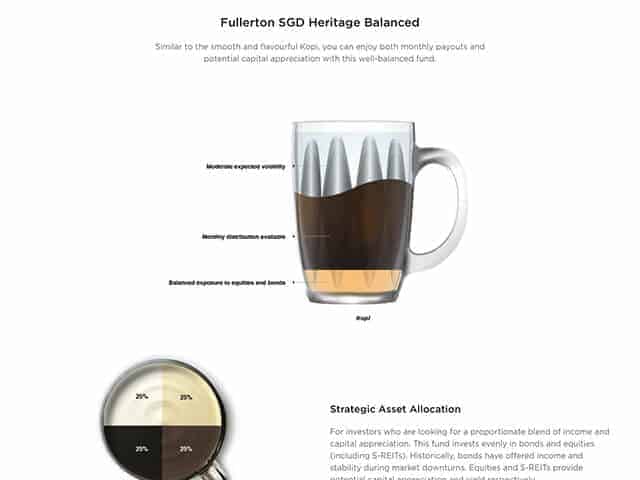
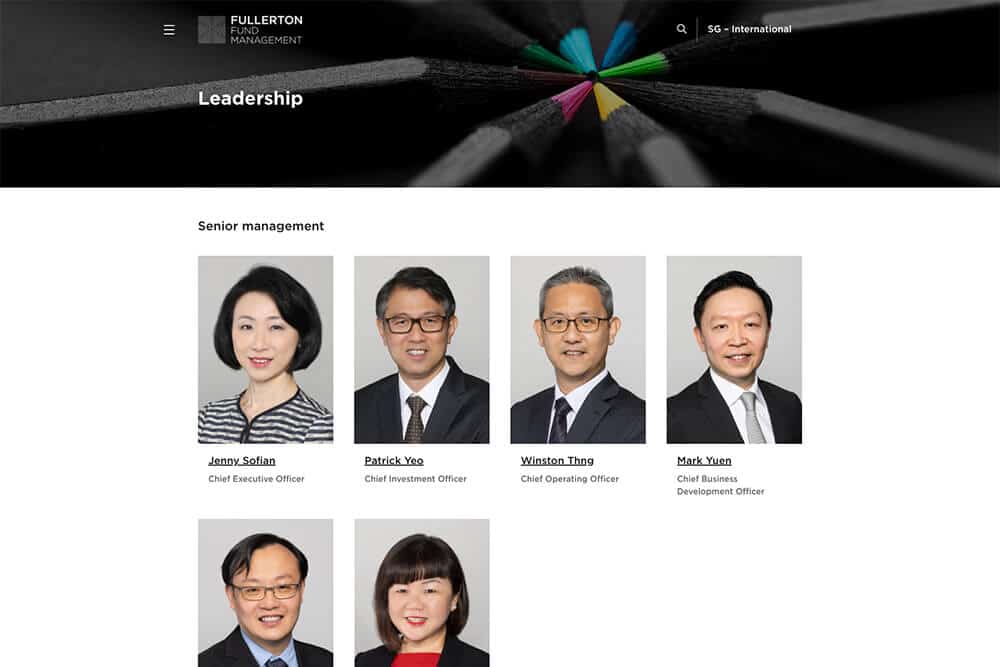
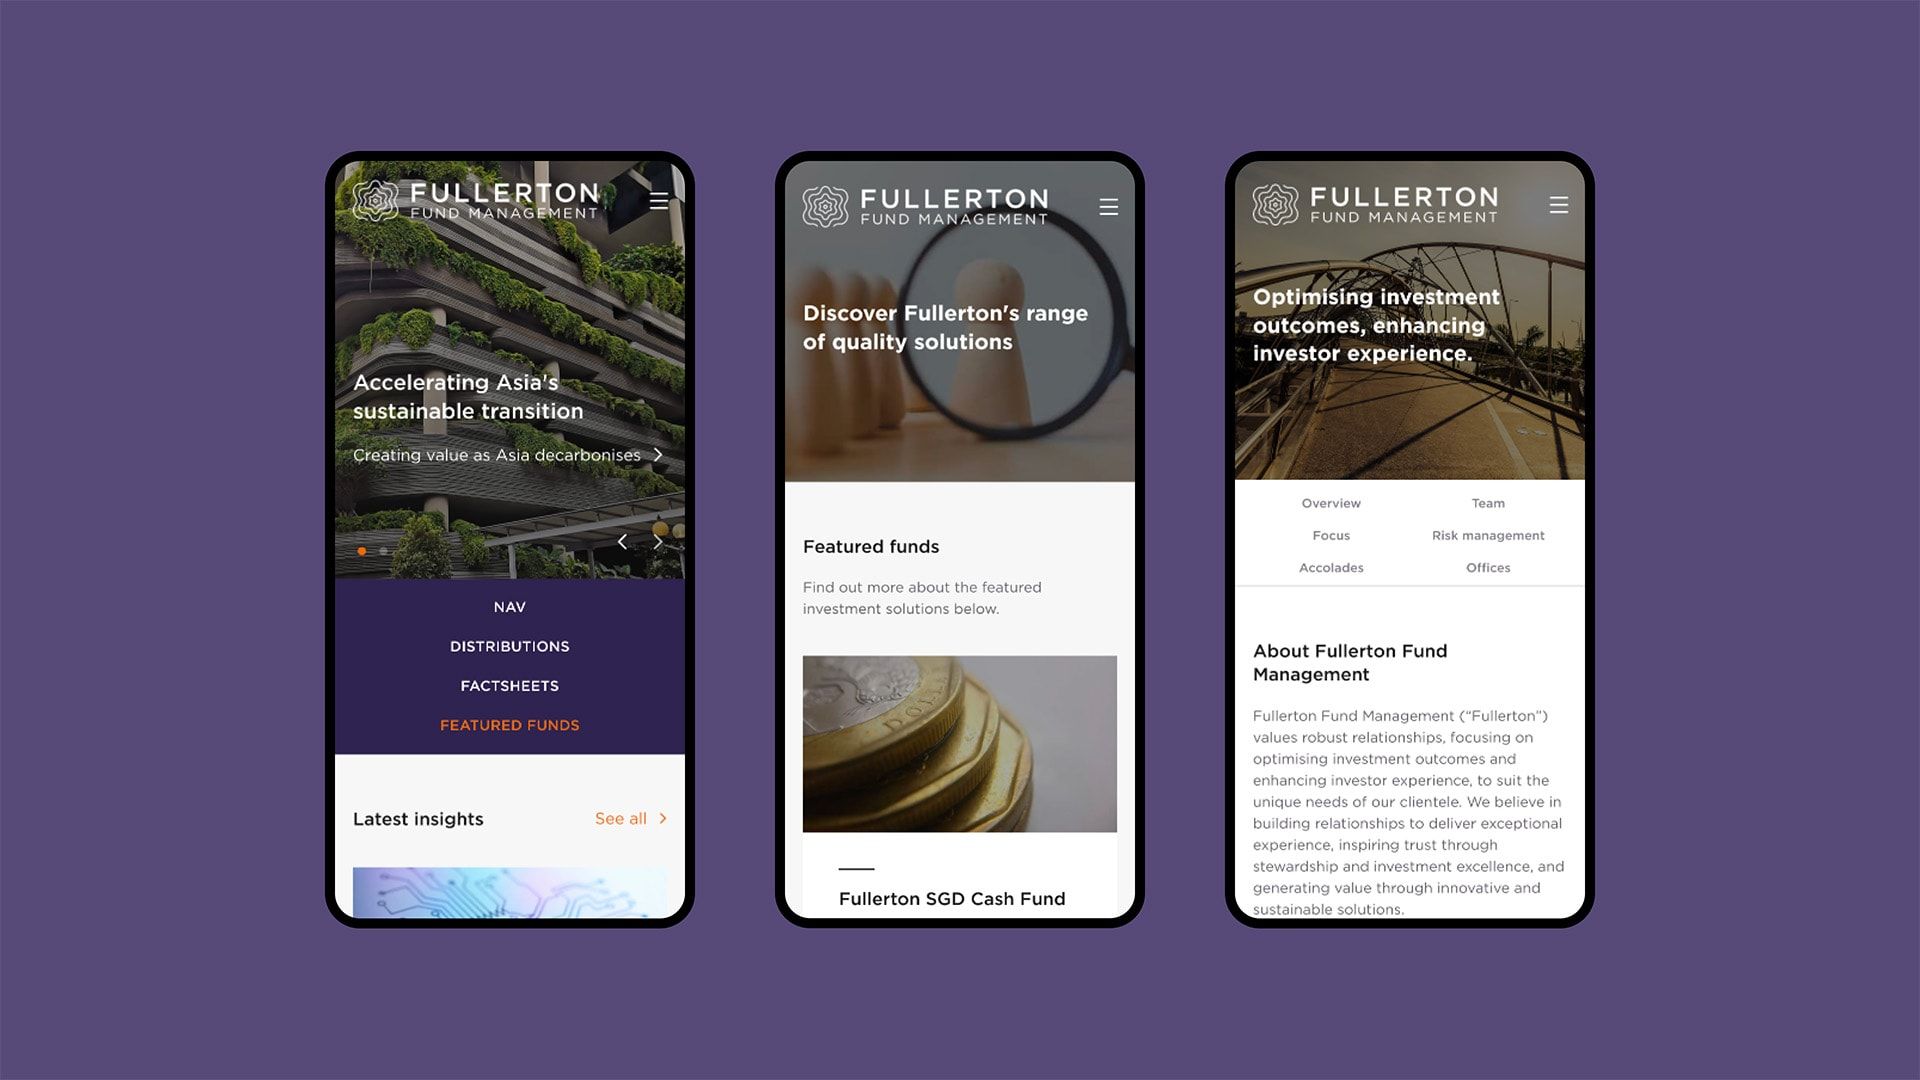
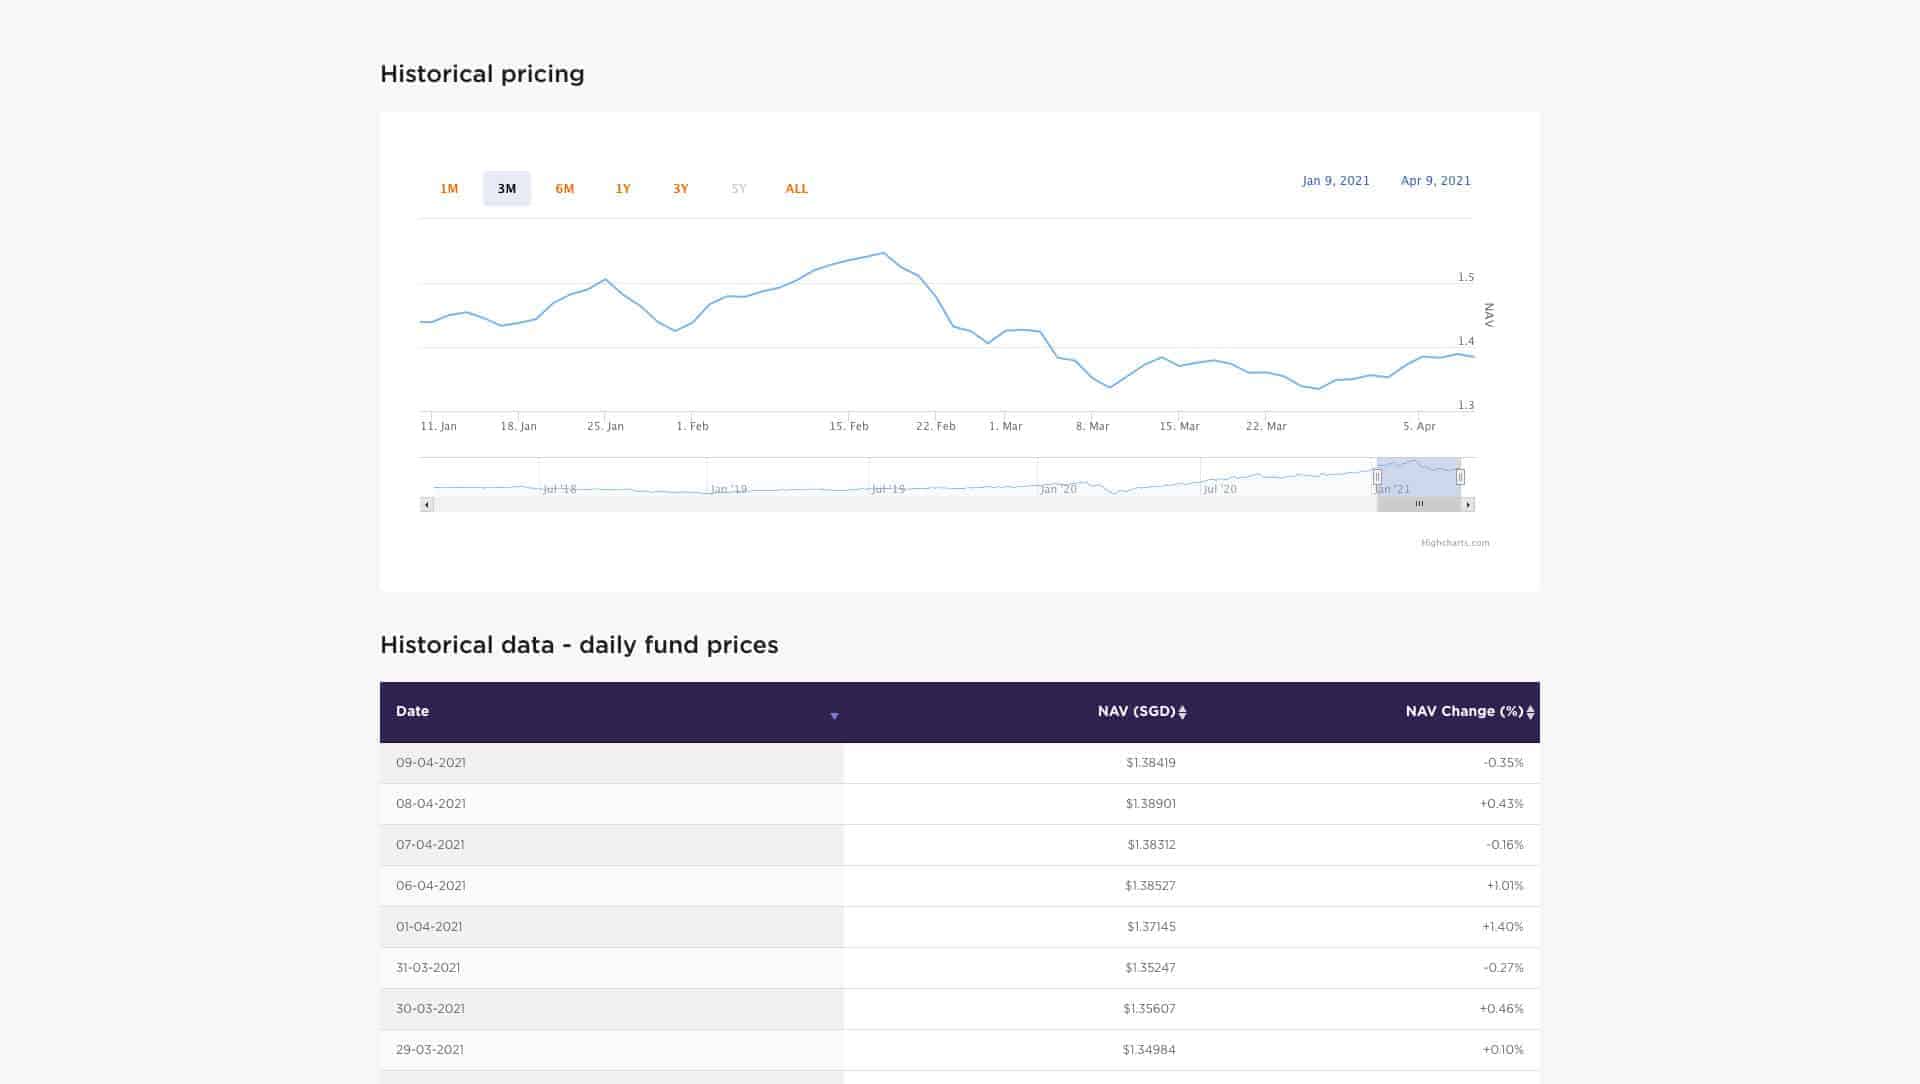
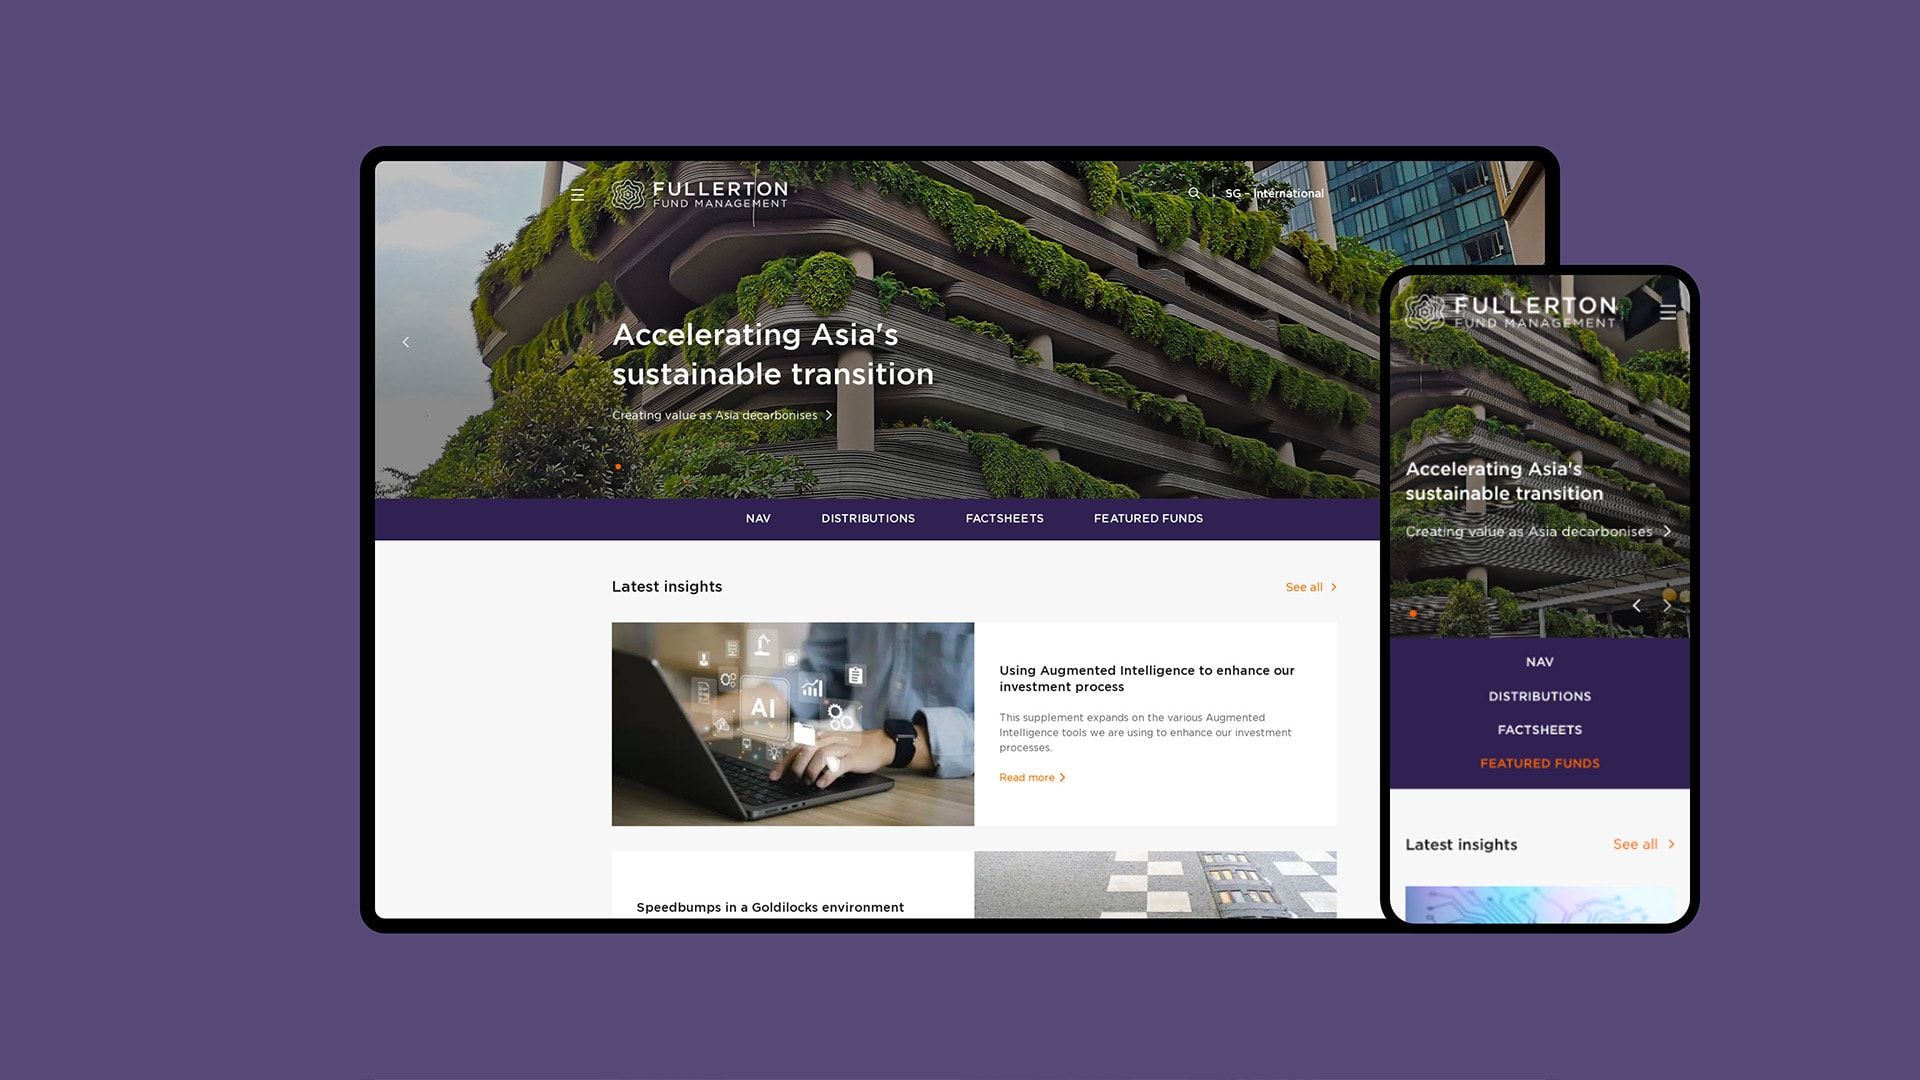
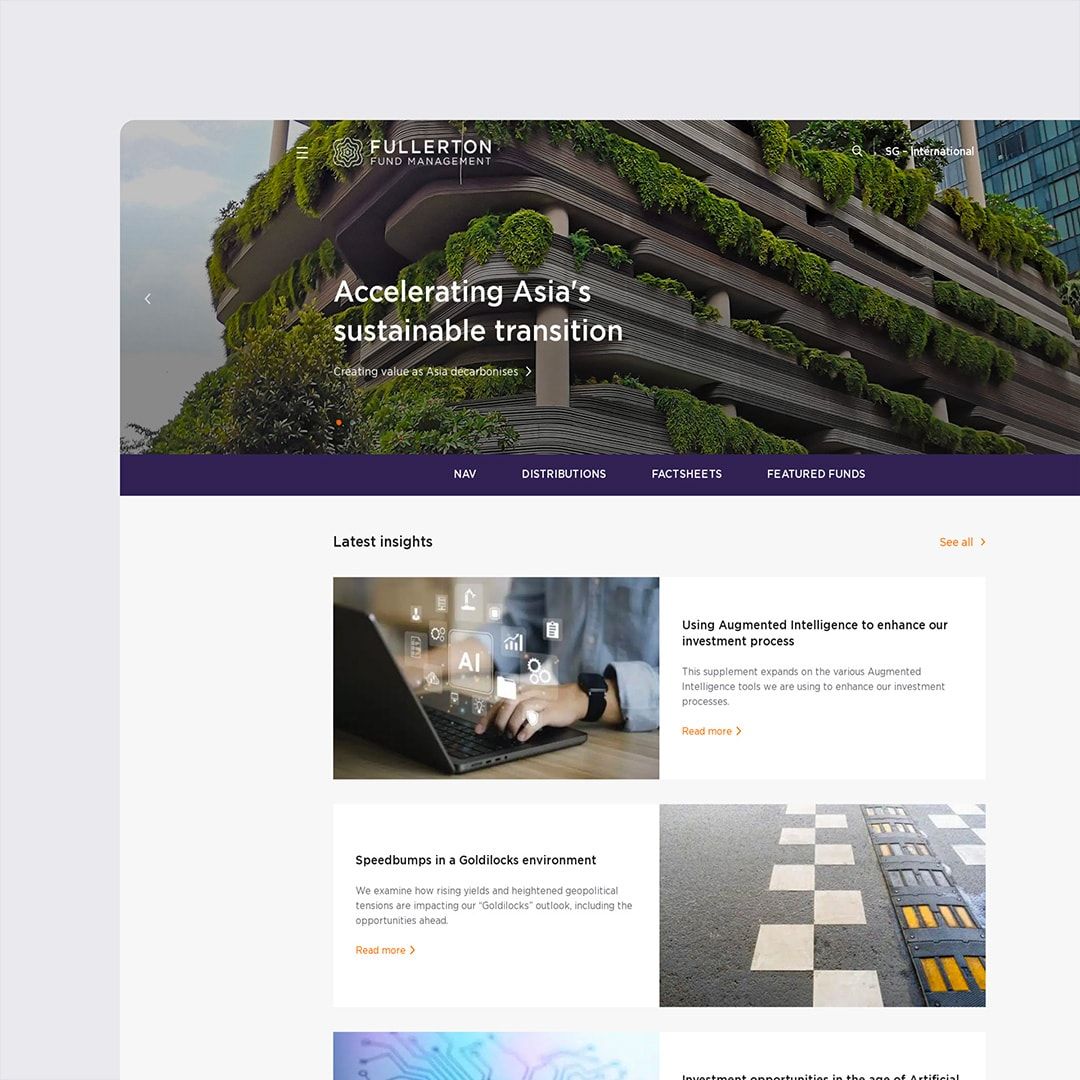
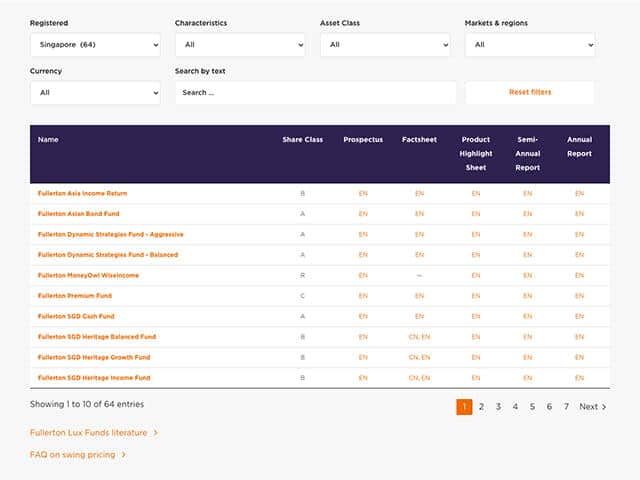
The engagement began in 2021 with a full redesign. We built a custom WordPress child theme on the Genesis Framework with Beaver Builder, structured as a Multisite so the team could publish insights and market commentary quickly. An enhanced Fund Centre put fund information within easy reach, and the information architecture led visitors from positioning through product pages to a clear call to action. Chillybin has hosted and maintained the platform since launch, so we were still in the room when the security requirements arrived.
Penetration test remediation, twice
In early 2024 Fullerton's penetration testing surfaced findings that we remediated: broken access control, vulnerable JavaScript libraries and server header configuration.
In 2025 the site moved from WP Engine to the Seviora Cloud Platform, its parent group's infrastructure. Between February and April we logged 44 hours migrating the site, re-implementing every earlier security fix and working through a fresh round of VAPT findings, including Content Security Policy headers. The production cutover took 6.5 hours on a Saturday, so the platform never went down during Asian market hours.
Ongoing care under a formal SLA
Post-migration, the relationship moved onto a documented care agreement: weekly core, plugin and theme updates deployed to UAT first and to production only after approval, daily encrypted off-site backups with one-click restore, uptime and security monitoring, and guaranteed response times during Singapore business hours and for after-hours emergencies. In 2026 we began a content refresh, cataloguing 132 published awards and 164 articles ahead of a new Investment Essentials section.

What we delivered
Fullerton now runs on infrastructure its group controls, on a platform that has passed two rounds of security review, with a partner who carries the history of every fix. The marketing team publishes insights without waiting on developers. Compliance stakeholders get staging, UAT and production kept separate, and every update approved before it reaches the live site. When the next audit or infrastructure change lands, the same team that built the site handles it.
What we learned
Security work for a regulated client is never finished, and it is never portable. The 2024 fixes were correct and complete, and the platform move still meant doing them again. Remediation lives in the infrastructure, not just the codebase, so whoever runs the migration needs to own the security history too.
Because we had hosted the site since 2021, the migration did not start with discovery. We already knew every plugin, header and caching rule, which is the difference between a 44-hour migration and a much longer one.
Impact & outcomes
penetration test cycles remediated
weekend cutover to the Seviora Cloud Platform
active users in the first nine months of 2026, up 83% year on year

